Azure 基于角色的访问控制(Azure RBAC) 是用于管理对 Azure 资源的访问的授权系统。 若要从 Azure 资源中删除访问权限,请删除角色分配。 本文介绍如何使用 Azure 门户、Azure PowerShell、Azure CLI 和 REST API 删除角色分配。
先决条件
若要删除角色分配,必须具有:
-
Microsoft.Authorization/roleAssignments/delete权限,例如 基于角色的访问控制管理员
对于 REST API,必须使用以下版本:
-
2015-07-01或更高版本
有关详细信息,请参阅 Azure RBAC REST API 的 API 版本。
Azure 门户
在要删除访问权限的作用域(例如管理组、订阅、资源组或资源)上打开 访问控制(IAM )。
单击“ 角色分配 ”选项卡可查看此范围中的所有角色分配。
在角色分配列表中,勾选要删除角色分配的安全主体旁边的复选框。
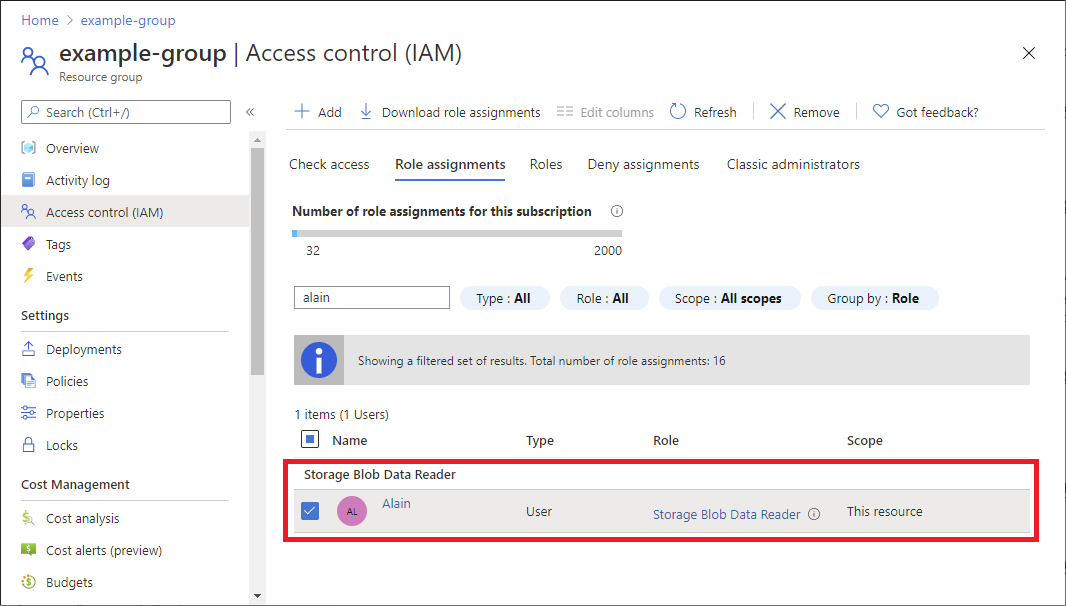
如果要删除在经典管理员停用过程中自动分配的 所有者 角色分配,角色分配具有以下说明。 有关更多信息,请参阅 “自动分配到所有者角色”。
- 描述:
The Classic Admin role was converted to an Azure Owner role on behalf of the user due to Classic Admin retirement
- 描述:
单击 “删除” 。
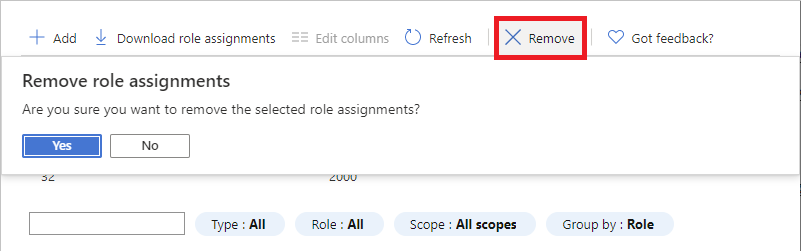
在显示的“删除角色分配”消息中,单击“ 是”。
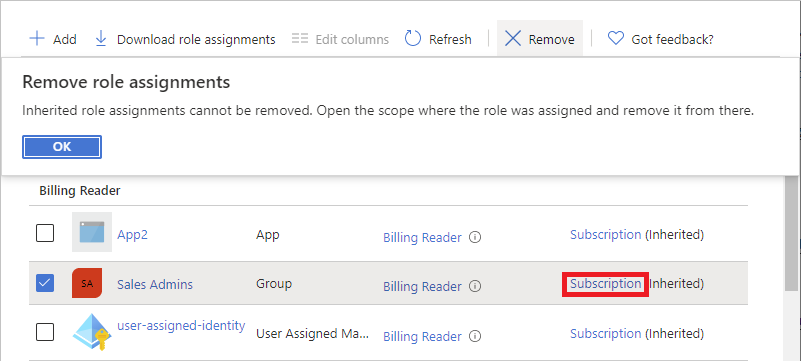
如果看到一条关于无法删除继承的角色分配的消息,说明您正在尝试删除子范围内的角色分配。 您应该在角色分配的具体范围内打开访问控制(IAM),然后重试。 在正确的范围内打开访问控制(IAM)的一种快速方法是查看 “作用域” 列,然后单击 (继承)旁边的链接。


Azure PowerShell
在 Azure PowerShell 中,使用 Remove-AzRoleAssignment 删除角色分配。
以下示例从patlong@contoso.com资源组上的用户中删除虚拟机参与者角色分配:
PS C:\> Remove-AzRoleAssignment -SignInName patlong@contoso.com `
-RoleDefinitionName "Virtual Machine Contributor" `
-ResourceGroupName pharma-sales
从订阅范围内 ID 为 22222222-2222-2222-2222-222222222222 的 Ann Mack 团队 组中删除 读者 角色。
PS C:\> Remove-AzRoleAssignment -ObjectId 22222222-2222-2222-2222-222222222222 `
-RoleDefinitionName "Reader" `
-Scope "/subscriptions/00000000-0000-0000-0000-000000000000"
从管理组范围的用户中移除 计费读取者 角色alain@example.com。
PS C:\> Remove-AzRoleAssignment -SignInName alain@example.com `
-RoleDefinitionName "Billing Reader" `
-Scope "/providers/Microsoft.Management/managementGroups/marketing-group"
从 ID 为 33333333-3333-3333-3333-333333333333 的主体中删除 ID 为 18d7d88d-d35e-4fb5-a5c3-7773c20a72d9 的 用户访问管理员 角色,在订阅范围 ID 为 00000000-0000-0000-0000-000000000000 内。
PS C:\> Remove-AzRoleAssignment -ObjectId 33333333-3333-3333-3333-333333333333 `
-RoleDefinitionId 18d7d88d-d35e-4fb5-a5c3-7773c20a72d9 `
-Scope /subscriptions/00000000-0000-0000-0000-000000000000
如果收到错误消息:“提供的信息不会映射到角色分配”,请确保还指定 -Scope 或 -ResourceGroupName 参数。 有关详细信息,请参阅 Azure RBAC 疑难解答。
Azure CLI
在 Azure CLI 中,使用 az role assignment delete 删除角色分配。
以下示例从patlong@contoso.com资源组上的用户中删除虚拟机参与者角色分配:
az role assignment delete --assignee "patlong@contoso.com" \
--role "Virtual Machine Contributor" \
--resource-group "pharma-sales"
从订阅范围内 ID 为 22222222-2222-2222-2222-222222222222 的 Ann Mack 团队 组中删除 读者 角色。
az role assignment delete --assignee "22222222-2222-2222-2222-222222222222" \
--role "Reader" \
--scope "/subscriptions/00000000-0000-0000-0000-000000000000"
从管理组范围的用户中移除 计费读取者 角色alain@example.com。
az role assignment delete --assignee "alain@example.com" \
--role "Billing Reader" \
--scope "/providers/Microsoft.Management/managementGroups/marketing-group"
REST API
在 REST API 中,通过使用 Role Assignments - Delete 删除角色分配。
获取角色分配标识符(GUID)。 首次创建角色分配时,将返回此标识符,也可以通过列出角色分配来获取该标识符。
从以下请求开始:
DELETE https://management.chinacloudapi.cn/{scope}/providers/Microsoft.Authorization/roleAssignments/{roleAssignmentId}?api-version=2022-04-01在 URI 中,将 {scope} 替换为删除角色分配的范围。
Scope 类型 providers/Microsoft.Management/managementGroups/{groupId1}管理组 subscriptions/{subscriptionId1}Subscription subscriptions/{subscriptionId1}/resourceGroups/myresourcegroup1资源组 subscriptions/{subscriptionId1}/resourceGroups/myresourcegroup1/providers/microsoft.web/sites/mysite1Resource 将 {roleAssignmentId} 替换为角色分配的 GUID 标识符。
该请求将删除在订阅范围内指定的角色分配:
DELETE https://management.chinacloudapi.cn/subscriptions/{subscriptionId1}/providers/microsoft.authorization/roleassignments/{roleAssignmentId1}?api-version=2022-04-01下面显示了输出示例:
{
    "properties": {
        "roleDefinitionId": "/subscriptions/{subscriptionId1}/providers/Microsoft.Authorization/roleDefinitions/a795c7a0-d4a2-40c1-ae25-d81f01202912",
        "principalId": "{objectId1}",
        "principalType": "User",
        "scope": "/subscriptions/{subscriptionId1}",
        "condition": null,
        "conditionVersion": null,
        "createdOn": "2022-05-06T23:55:24.5379478Z",
        "updatedOn": "2022-05-06T23:55:24.5379478Z",
        "createdBy": "{createdByObjectId1}",
        "updatedBy": "{updatedByObjectId1}",
        "delegatedManagedIdentityResourceId": null,
        "description": null
    },
    "id": "/subscriptions/{subscriptionId1}/providers/Microsoft.Authorization/roleAssignments/{roleAssignmentId1}",
    "type": "Microsoft.Authorization/roleAssignments",
    "name": "{roleAssignmentId1}"
}
ARM 模板
无法使用 Azure 资源管理器模板(ARM 模板)删除角色分配。 若要删除角色分配,必须使用其他工具,例如 Azure 门户、Azure PowerShell、Azure CLI 或 REST API。